RISK
RESILIENCE
Cyber resilience is a leadership decision.
NIS2 connects critical services, cybersecurity measures, incident reporting and management accountability. Understand who may be in scope, then organise the work across teams.
Start with the organisation, not the acronym.
Sector is only one part of the question. Entity type, size, exceptions, establishment and national law all shape the analysis.
How to assess scope ↗Resilience has to be owned.
Connect management decisions to the services at risk, the measures in operation and the evidence of review.
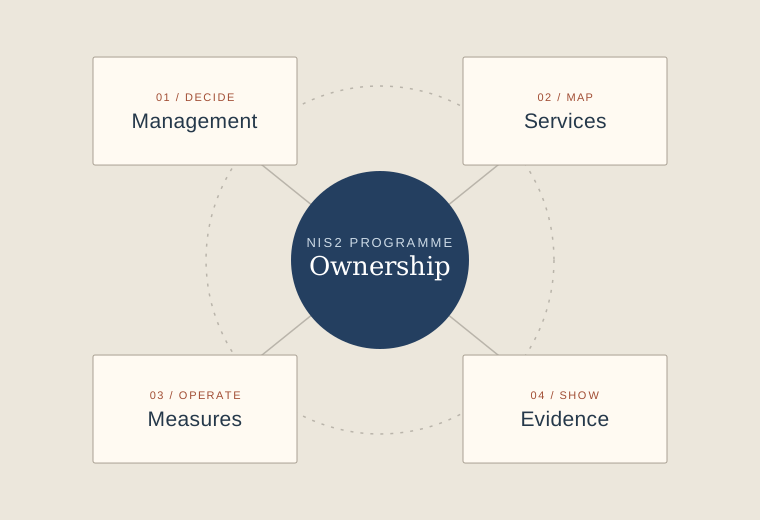
Management
Make approvals, oversight and training visible.
Services
Understand what the organisation needs to keep running.
Measures
Assign owners to risk management and incident preparation.
Evidence
Keep decisions, tests and follow-up in a usable record.
Four workstreams to organise.
Cybersecurity risk management
Build proportionate measures around risk analysis, policies, incident handling, continuity, supply chain and other areas listed in Article 21.
02Incident reporting
Prepare to assess significant incidents and make staged notifications through the relevant national route.
03Management accountability
Management bodies have a role in approving and overseeing cybersecurity risk-management measures and receiving relevant training.
04Supply-chain security
Consider security-related aspects of relationships with direct suppliers and service providers within the risk-management measures.
Know the reporting path before the clock starts.
Article 23 describes staged notification for significant incidents. Confirm the applicable national channel and the circumstances of the event.
Early warning
After awareness of a significant incident, subject to the Directive’s conditions.
Incident notification
An initial assessment updates the early warning where applicable.
Final report
Generally measured after notification; Article 23 gives the detail and exceptions.
Move from interpretation to operation.
A practical route gives every phase an owner and an output. A generic checklist alone cannot establish compliance.
Scope
Map entities and services
Assess
Review risks and measures
Prioritise
Assign decisions and owners
Operate
Test, document and review
Working notes for the decisions ahead.
Starting a NIS2 scope review
A useful scope review begins with the services you provide, the legal entities involved and where those services operate.
02 / GovernanceEvidence for management oversight
Executive oversight is easier to demonstrate when risk decisions, owners and follow-up actions are recorded as part of normal governance.
03 / Incident reportingPreparing an incident notification workflow
A reporting clock is difficult to manage without clear triage, escalation and ownership before an incident happens.